


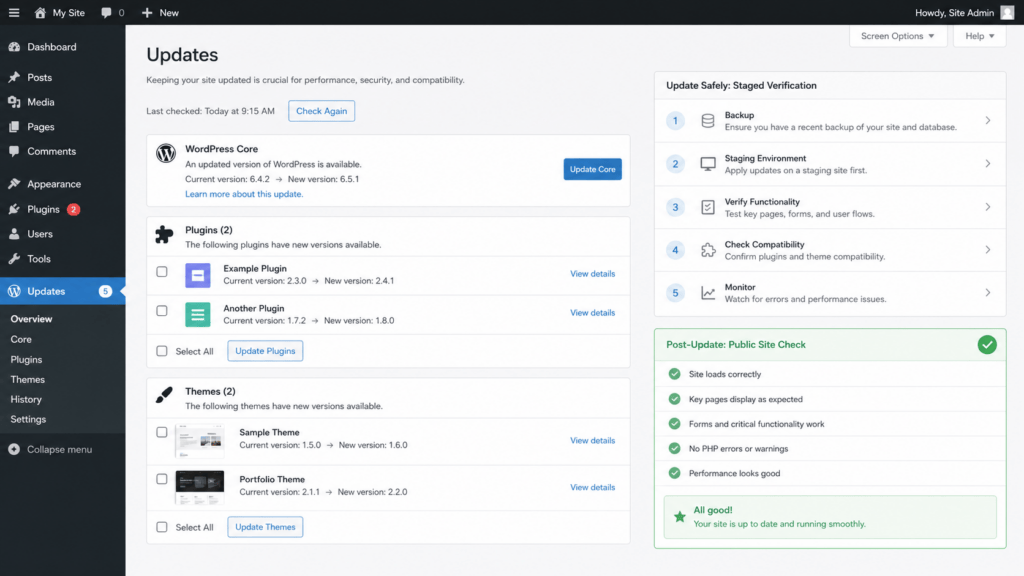
October 2026 update: WordPress 7.1.3 is a maintenance and security release. Use the normal managed-host or WordPress maintenance process to install the current supported core release.
After the update, confirm the installed version and test the site’s important public and logged-in paths. If a site remains on an older eligible branch, check the official release information for that branch’s backport before marking the work complete. This is a patch-and-verify task; the release notice alone does not establish that a particular site was attacked.
What site owners should know
The official WordPress 7.1.3 notice describes maintenance and security updates and says necessary security backports for eligible older branches are in progress and will ship as they become ready. Follow the normal patch-and-verify process for the release in use; the notice does not establish that a particular site was attacked.
Start with your WordPress dashboard or managed host panel. Record the installed core version, the active theme, and any pending plugin or PHP compatibility notices. If your host handles automatic core updates, confirm the completed version rather than assuming the job has run. For a site held on an older branch, check the exact branch’s fixed release before marking it protected.
Update without losing your recovery path
- Confirm a usable recovery point. Check that the normal backup or host restore service has a recent recovery point and that the restore process is understood. A successful job notification is not the same as a tested restore. See our WordPress backup verification guide.
- Choose a short maintenance window. Tell the people responsible for publishing, forms, bookings, or orders when validation will occur. Use staging for sites with custom themes, complex plugins, or critical transactions. Our update-window checklist covers that preparation.
- Install the official update. Use the WordPress Updates screen or your managed host’s supported update path. Avoid third-party packages or emergency code changes that have not been reviewed.
- Verify the installed version and visitor paths. Recheck core version in the dashboard. Visit the public homepage and representative posts, sign in to the editor, submit a test form, and test checkout or booking flows where they exist. Check mobile rendering and any multilingual or member-only paths that matter to your site.
- Clear caches and watch for errors. Purge the site’s normal page cache and CDN cache when the update is complete. Review your host’s application and security alerts for unexpected errors, then document the version and test results for the site owner.
If the update cannot be completed yet
Escalate the version and compatibility blocker to the host or site maintainer promptly. Keep existing security controls enabled and limit unnecessary administrative access while preparing the supported update path. Do not treat a firewall rule, a lack of visible errors, or an unverified backport as proof that core is patched. If you suspect compromise, preserve the normal incident records and have an authorized responder review the site before making broad changes.
Need help planning the update or checking the result? Start with Fix I.T. Phill WordPress support. For the release and its current branch guidance, use the official WordPress 7.1.3 announcement.