Salon Booking System WordPress Plugin CVE-2026-110032 Update Guide
October 19, 2026
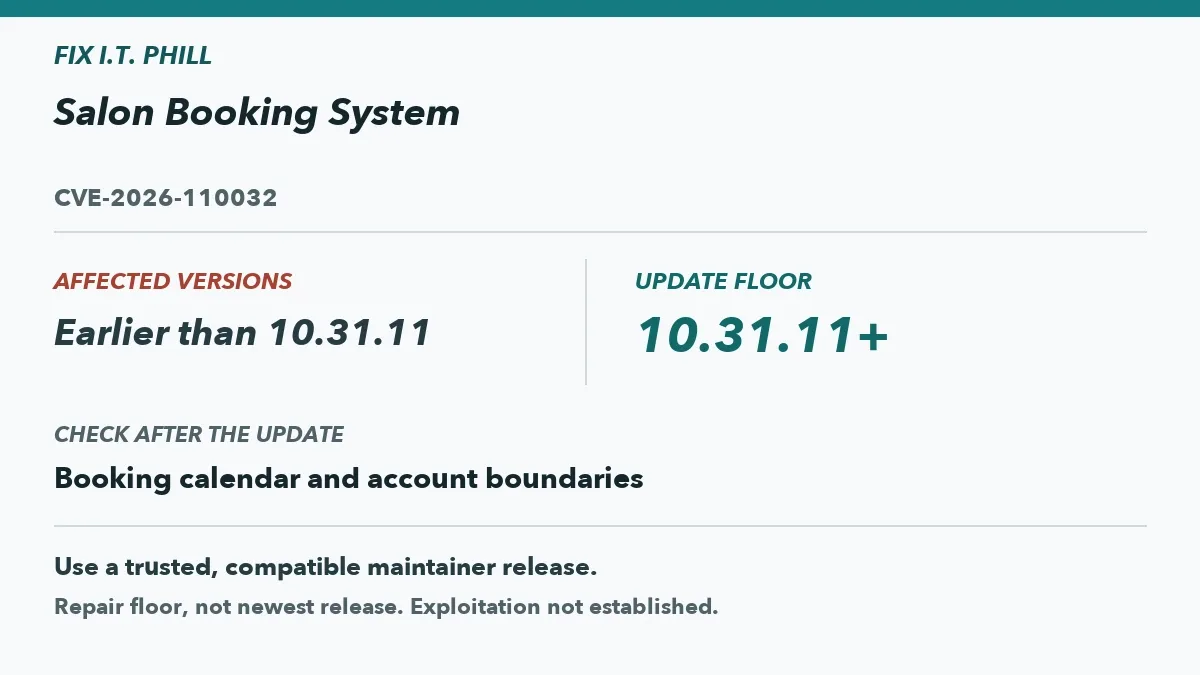
CVE-2026-110032 affects the Salon Booking System WordPress plugin before version 10.31.11. Update affected installations to 10.31.11 or later using a trusted, compatible maintainer release. Incorrect authorization could allow authorized salon staff roles to alter other accounts, with consequences including role changes, profile modification and loss of administrative access. Exploitation has not been established.
Identify sites below the repair floor
For each site using Salon Booking System, check the installed plugin version in the normal WordPress Plugins and Installed Plugins view. Versions earlier than 10.31.11 need the documented update; sites without the plugin are not in scope for this advisory.
A version check helps prioritize maintenance but does not establish that accounts were altered. Keep the assessment focused on CVE-2026-110032 rather than drawing conclusions about unrelated plugins or the wider WordPress installation.
- Before 10.31.11: update is needed.
- 10.31.11 or later: the stated repair floor is met.
- The repair floor is not necessarily the latest plugin version.
Install a compatible trusted update
Use the organization’s normal WordPress maintenance process and a trusted compatible release from the plugin maintainer to update to 10.31.11 or later. Confirm the installed version when maintenance is complete, and resolve compatibility issues through normal vendor or hosting support arrangements.
Treat the update floor as a targeted remediation threshold, not as independent testing of the site or a guarantee about other extensions. Routine backup, change-control, and recovery practices remain important during plugin maintenance.
Validate account boundaries with safe test data
In authorized staging, use synthetic data to confirm that the booking calendar works as intended after the update. Also confirm that salon staff and administrator accounts retain only their intended boundaries and that legitimate administrative access remains available.
Review unexplained account changes using available administrative history and existing security procedures. Since exploitation is not established, avoid assuming either misuse or its absence without supporting evidence. Escalate concrete concerns through the site’s normal incident process.